Vibe-coded it fast?StackShield checks it before launch.
Pre-launch security for apps built with Lovable, Bolt, v0, Cursor, or Replit. Catch leaked keys, broken RLS, and open CORS before your first real user does.
Built with the best tools
 React.js19
 Typescript5.7
 Shadcn2.0
 Tailwind CSS4
Ship secure apps, faster.
Leaked keys, caught instantly
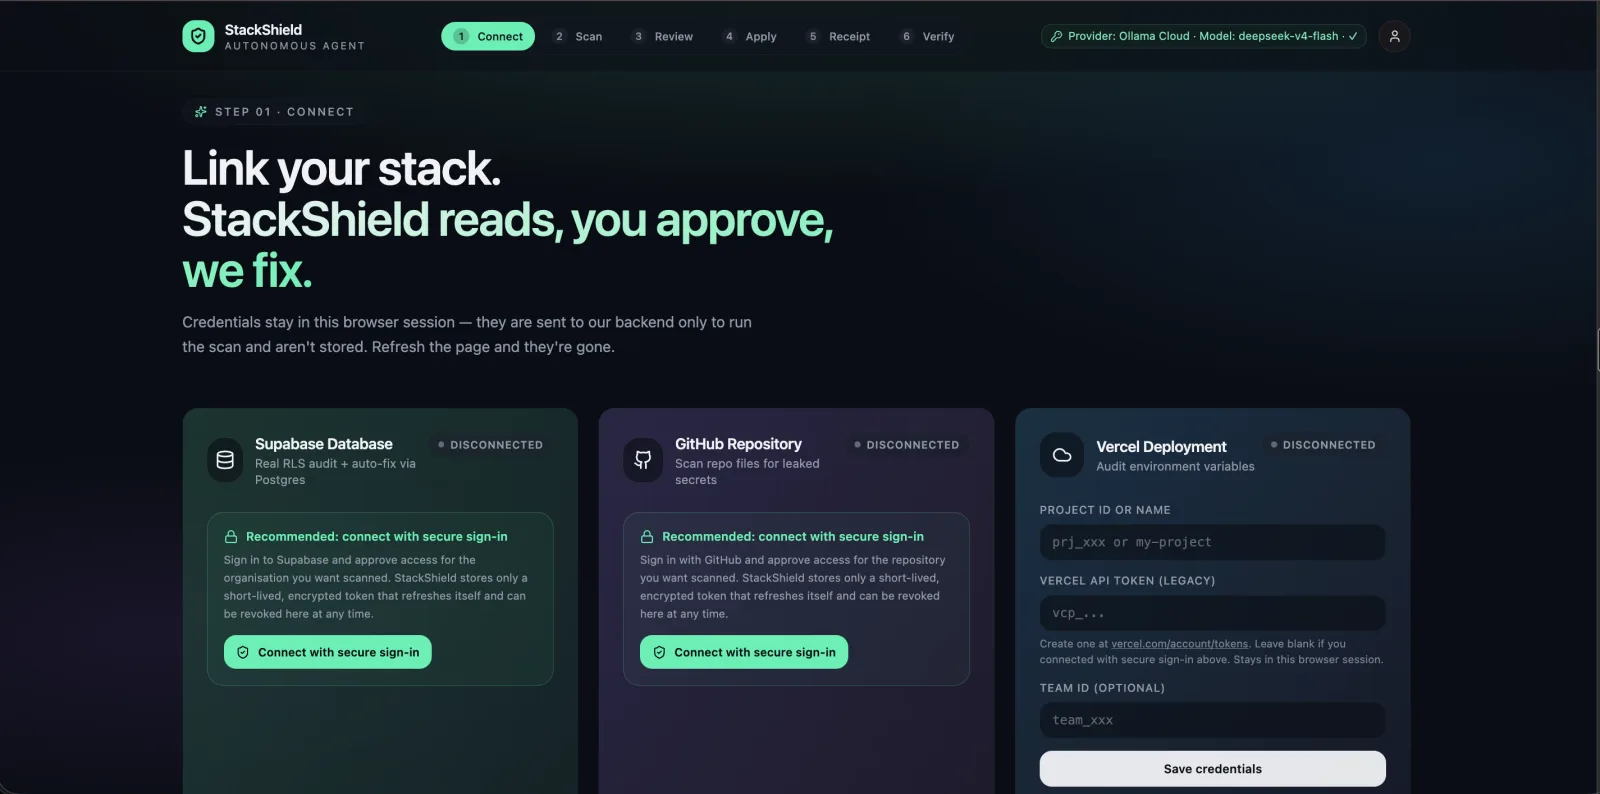
Scans your GitHub repo, Supabase env, and Vercel config for exposed API keys, tokens, and secrets before any user hits your app.
You review, we fix
Every finding comes with an AI-generated fix. You review and approve — StackShield applies it directly to your repo, database, or deployment.
Fits your vibe-coded stack
Built for Lovable, Bolt, v0, Cursor, and Replit projects — no custom setup or complicated integrations.
Connect in one click, scan in seconds.
Your credentials, encrypted and scoped
Credentials are stored encrypted (AES-256-GCM) and used only for scanning. Disconnect anytime to revoke access.
Scan results are kept for 30 days to detect security drift. Delete your account to remove all data.
We need to update this heading before launch
Let me quickly jump in and fix it
Done!
Everything you need.
Nothing you don't.

Supabase RLS audits
Automatically checks every Postgres table for missing or broken Row-Level Security policies.

GitHub secrets sweep
Scans your entire repository for leaked API keys, tokens, passwords, and other sensitive strings.

Vercel env inspection
Reviews your Vercel deployment environment variables for exposed secrets and misconfigurations.

CORS misconfiguration
Catches open CORS headers that would let any site read your API responses.

AI-powered auto-fixes
Every finding ships with a one-click AI fix — review it, approve it, and it's applied instantly.

Production Readiness PDF
Get a step-by-step hardening checklist you can share with your team or investors.

Works with any AI provider
Bring your own Ollama Cloud, OpenAI, or Anthropic key — AI costs stay yours.

Full audit receipt
Download a complete log of every scan, finding, and fix applied for your records.
Security you can trust.
And ship on.
Every scan is thorough, every fix is reviewed by you, and every receipt is yours to keep. StackShield is built on trust — no surprises, no lock-in.

Make the right impression
StackShield runs pre-launch security checks so you can ship your vibe-coded app with confidence — no pentest required.
Supabase
Project: my-app-prod
GitHub
Repo: santa4324/my-app
Vercel
Project: my-app-prod
Simple, transparent pricing.
Scan for free, fix with AI on a plan. No hidden fees. AI costs stay with your provider.
Free
For everyone starting out — no card needed, no expiry.
No credit card required
Supabase, GitHub & Vercel scanning
Manual on-demand scans
Security findings report
No AI auto-fixing

Starter
For indie devs and solo founders shipping their first product.
Cancel anytime
Unlimited scanning, all integrations
20 AI auto-fixes per month
Bring your own AI provider key
Email support
Production Readiness Checklist PDF

Pro
For teams and agencies shipping multiple products.
Cancel anytime
Unlimited scanning, all integrations
200 AI auto-fixes per month
Bring your own AI provider key
Priority processing & support
Production Readiness Checklist PDF
Questions and Answers
Start building